Raidefend Technologies provides IT security and infrastructure services to businesses of all sizes. We partner with leading tech providers to deliver tailored, reliable, and secure solutions that drive success.

Gallery

Contacts

Meydan Freezone - Al Meydan Rd - Nad Al Sheba , Dubai

support@raidefend.com

800 48 2273

SentinelOne
Your local security partnerRAIDEFEND TECHNOLOGIES
AI-powered security. Local expertise.

SentinelOne Partner
in Dubai & UAE.

Protect your endpoints, cloud workloads, and identities with the Singularity Platform. RAIDEFEND helps you evaluate, deploy, and manage SentinelOne across the UAE and Saudi Arabia.

Endpoint & XDRCloud & identityAI-powered investigations
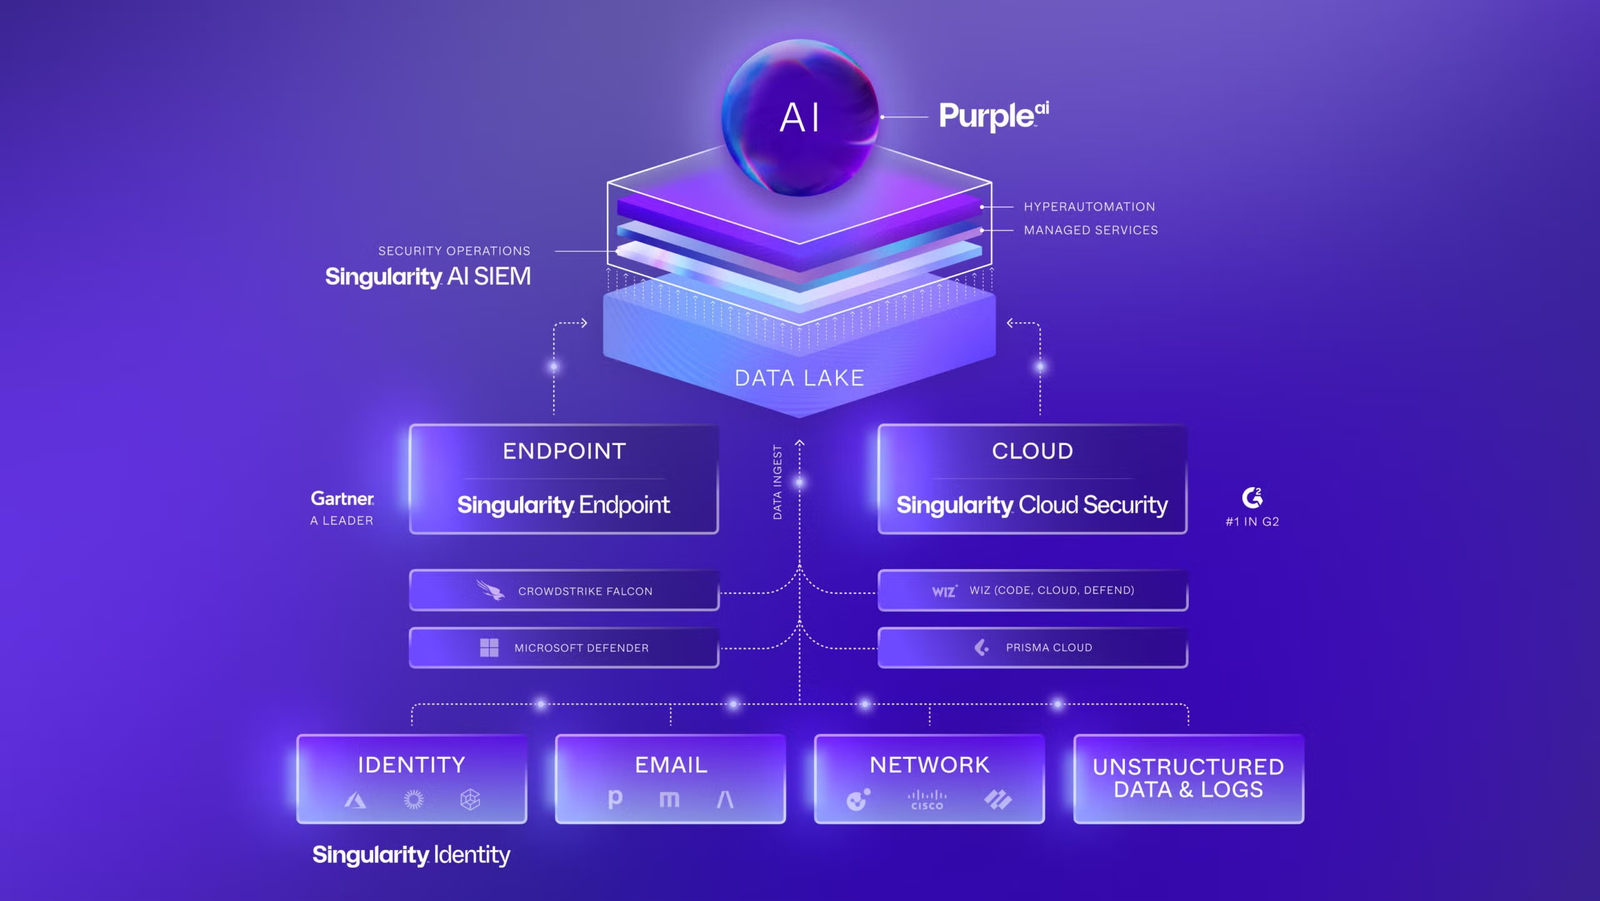
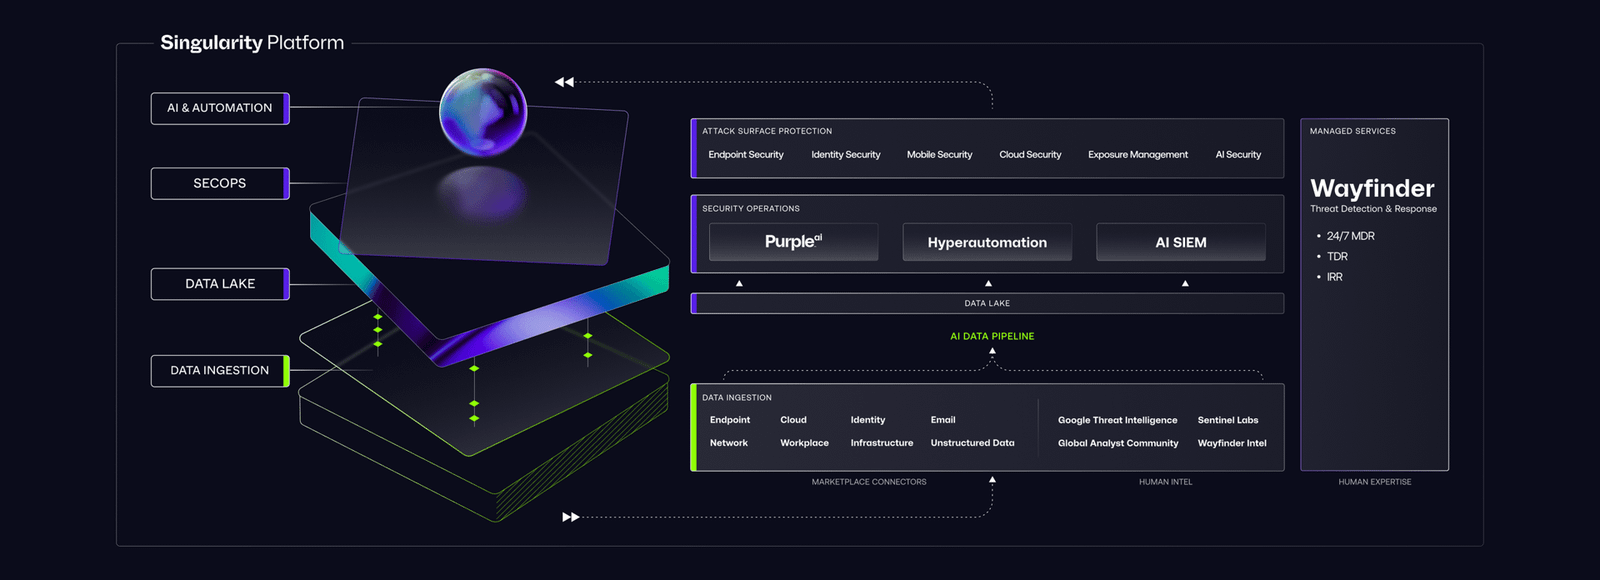
SentinelOne Singularity Platform architecture connecting attack surface protection, security operations, data lake, and managed services
One Singularity Platform● Endpoint● Cloud● Identity● AI SIEM● Purple AI
SentinelOne. Delivered by RAIDEFEND.

Your SentinelOne partner in UAE.
From planning to protection.

Based in Dubai, RAIDEFEND Technologies helps businesses deploy and manage the SentinelOne Singularity Platform. We bring endpoint, cloud, and identity security together around your environment and your security priorities.

From solution selection and demonstrations to implementation and ongoing support, our team works with organizations in Dubai, Abu Dhabi, across the UAE, and the wider GCC.

Discuss your SentinelOne requirements
The Singularity Platform

Connected security.
Across your attack surface.

Bring prevention, detection, investigation, and response into one platform, with the capabilities your business needs.

01 / ENDPOINT

Singularity Endpoint

AI-powered endpoint protection and EDR help your team detect suspicious activity, investigate incidents, and respond across devices and servers.

  • Behavioral AI threat detection
  • Storyline investigation context
  • Windows, macOS, and Linux coverage
02 / CLOUD

Singularity Cloud Security

Gain visibility into cloud risks and protect workloads and containers with cloud security designed for modern environments.

  • Cloud posture and exposure visibility
  • Verified Exploit Paths
  • Runtime threat protection
03 / IDENTITY

Singularity Identity

Identify risky identity exposures and help detect credential misuse, reconnaissance, and lateral movement.

  • Identity exposure assessment
  • Identity threat detection and response
  • Deception to reveal attack activity
04 / SECURITY OPERATIONS

Singularity AI SIEM

Bring security data together to strengthen visibility, accelerate investigation, and support AI-driven detection and response.

  • Centralized security data and analytics
  • Real-time detection workflows
  • AI-assisted security operations
05 / AI FOR DEFENDERS

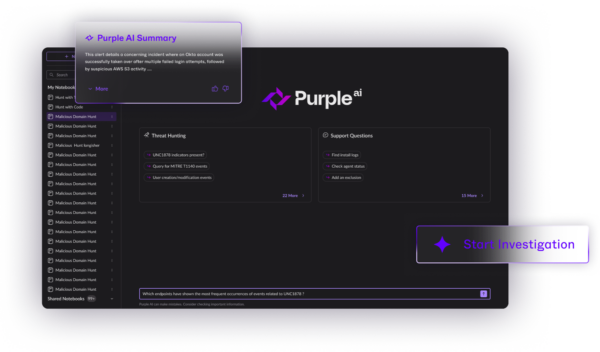
Purple AI

Turn natural-language questions into faster threat investigations. Give analysts useful context, summaries, and guidance to focus on the risks that matter.

  • Natural-language threat hunting
  • Investigation summaries and suggested queries
  • Connected security workflows
SentinelOne Purple AI interface for threat investigation
Purple AI · Existing SentinelOne product interface

Capabilities depend on the selected products, licensing, and deployment. RAIDEFEND helps map the right scope to your requirements.

Unified security architecture

One platform.
A connected view of security.

Bring native security data and connected tools together for visibility, investigation, and response across your environment.

SentinelOne Singularity architecture showing Purple AI, AI SIEM, Data Lake, endpoint, cloud, and connected security data
Singularity Endpoint

Endpoint security.
Built for the way you work.

Protection, investigation, and response across your endpoint environment.

Unified Agent

A lightweight agent brings endpoint protection and supported identity capabilities together, with simplified management and consistent visibility.

Behavioral AI Models

Detect suspicious and malicious activity patterns in real time across endpoints, servers, and cloud workloads.

Purple AI

Accelerate threat hunting and investigation with natural-language queries, useful summaries, and AI-assisted analyst workflows.

Storyline Technology

Connect related endpoint events into a clear timeline to understand how an attack started and what happened next.

1-Click Rollback

Help restore affected files and reverse malicious changes with one-click rollback on supported Windows configurations.

OS Coverage

Protect supported Windows, macOS, and Linux environments with centralized endpoint visibility and management.

The value of Singularity

Built for visibility.
Designed for action.

01

One platform, less complexity

Bring security visibility and response together to simplify operations and reduce tool fragmentation.

02

Protection built for modern threats

Use behavioral AI and endpoint telemetry to detect suspicious activity and support rapid containment.

03

AI that supports your analysts

Accelerate investigation and threat hunting with useful context and AI-assisted workflows.

04

Security across cloud workloads

Connect cloud visibility with runtime protection for workloads and containers.

05

An open security ecosystem

Integrate with existing security tools and correlate data to get more from your environment.

06

Faster, coordinated response

Use policy-based automation to reduce manual work and respond consistently to detected threats.

Your implementation journey

Local expertise.
At every stage.

Work with RAIDEFEND to turn your SentinelOne requirements into a practical deployment plan.

01

Understand

Review your endpoints, servers, cloud workloads, identity environment, and security goals.

02

Evaluate

Align the solution and licensing with your use cases, and explore the platform through a demo.

03

Deploy

Plan implementation, configure protection policies, and validate visibility and response workflows.

04

Support

Help your team manage the platform, review policies, and address operational requirements.

Dubai · Abu Dhabi · Across the UAE

SentinelOne Partner
in Dubai & UAE

Looking for a SentinelOne partner in Dubai or elsewhere in the UAE? RAIDEFEND helps businesses select, implement, and support endpoint security, XDR, cloud security, and identity protection.

Discuss your environment with our Dubai-based team to plan the right SentinelOne solution for your organization.

DubaiAbu DhabiUAE
Speak with our UAE team
Saudi Arabia · Wider GCC

SentinelOne Partner
for Saudi Arabia

Organizations seeking a SentinelOne partner in Saudi Arabia can work with RAIDEFEND to explore the Singularity Platform and plan endpoint, cloud, and identity security requirements.

Our regional approach also supports discussions with businesses in Qatar, Oman, Bahrain, and Kuwait, with deployment and support scope agreed around each project.

Saudi ArabiaQatar & OmanBahrain & Kuwait
Discuss your regional requirements

Explore SentinelOne’s industry recognition

Review analyst recognition and independent evaluations to support your security platform assessment.

View SentinelOne recognition

See what SentinelOne
can do for your business.

Discuss your requirements with RAIDEFEND.

// WHY TO CHOOSE

WHY CHOOSE SENTINELONE ?

Recognized by Industry Leaders

Gartner Peer Insights
Recognized as a Customers’ Choice for Endpoint Protection Platforms, with a 4.7 out of 5 rating based on hundreds of verified customer reviews.

Gartner Magic Quadrant
Named a Leader for five years running in the Magic Quadrant™ for Endpoint Protection Platforms, reflecting strong execution and long-term vision.

MITRE Engenuity
Record-breaking ATT&CK® Evaluations with AI-powered protection, achieving 100% detection in real time and #1 ranking on MITRE evaluations.

// faq

Sentinel One: Frequently Asked Questions

Is Raidefend Technologies an official SentinelOne partner?

Yes, Raidefend is SentinelOne partner supporting customers in the UAE and across GCC countries, including Saudi Arabia, Qatar, Oman, Bahrain and Kuwait.

What is SentinelOne and what makes it different from traditional antivirus

SentinelOne is an AI-powered cybersecurity platform that delivers autonomous endpoint, cloud, identity, and data protection. Unlike traditional antivirus that relies on signature-based detection, SentinelOne uses behavioral AI to detect and neutralize threats in real time  including zero-day attacks, fileless malware, and ransomware  without requiring human intervention.

What is the difference between EDR, XDR, and MDR?

EDR (Endpoint Detection & Response) focuses on endpoints only. XDR (Extended Detection & Response) extends protection across endpoints, cloud, identity, and network in a unified platform. MDR (Managed Detection & Response) adds a 24/7 human SOC layer on top. SentinelOne offers all three within its Singularity platform

Can SentinelOne detect and respond to threats without an internet connection?

Yes. SentinelOne's agent-centric architecture operates locally on every endpoint, enabling full threat detection, prevention, and autonomous response even when systems are completely offline or disconnected from the internet.

What types of threats does SentinelOne protect against?

SentinelOne protects against ransomware, zero-day exploits, fileless malware, supply chain attacks, insider threats, APTs (Advanced Persistent Threats), and AI-driven cyberattacks. Its behavioral AI continuously monitors all endpoint activity to catch threats that signature-based tools completely miss.

What is autonomous remediation and how does SentinelOne handle it?

When SentinelOne detects a threat, it autonomously quarantines it, kills malicious processes, and rolls back any damage caused by ransomware or malware to a clean state  all within seconds, without waiting for human intervention.

What is SentinelOne Singularity XDR?

Singularity XDR unifies endpoint, cloud, identity, and network telemetry into a single AI-powered platform with a centralized Security Data Lake. It provides complete enterprise-wide visibility, automated threat correlation, and faster incident response  eliminating the silos created by managing multiple disconnected security tools.

How does SentinelOne use AI and machine learning?

SentinelOne's AI engine runs multiple machine learning models simultaneously on every endpoint — analyzing process behavior, memory activity, network connections, and file operations in real time. The AI learns normal behavior patterns and flags anomalies autonomously, detecting both known threats and never-before-seen attacks without relying on threat signatures.

Can SentinelOne replace our existing SIEM or work alongside it?

SentinelOne's built-in Security Data Lake functions as a lightweight SIEM alternative for many organizations. For enterprises already running a SIEM, SentinelOne integrates natively with platforms like Splunk, Microsoft Sentinel, and IBM QRadar to enrich existing security operations.

What is Purple AI?

Purple AI is SentinelOne's generative AI security analyst that allows security teams to investigate incidents and hunt for threats using plain natural language instead of complex query languages. It dramatically accelerates investigations and reduces analyst workload.

How does SentinelOne support regulatory compliance?

SentinelOne provides comprehensive compliance reporting, forensic investigation capabilities, and detailed audit logs supporting GDPR, HIPAA, PCI-DSS, ISO 27001, UAE NESA, and Saudi NCA requirements. Its real-time visibility and automated incident response documentation significantly reduce compliance audit effort.​

How does SentinelOne reduce the total cost of cybersecurity operations?

SentinelOne consolidates antivirus, EDR, XDR, SIEM, and threat hunting into a single unified platform — eliminating the cost of managing separate tools. Its autonomous remediation reduces incident response time by up to 80%, lowers analyst workload, and significantly reduces the business impact of ransomware and cyberattacks.

    Ready to Get Started?

    Your email address will not be published. Required fields are marked *